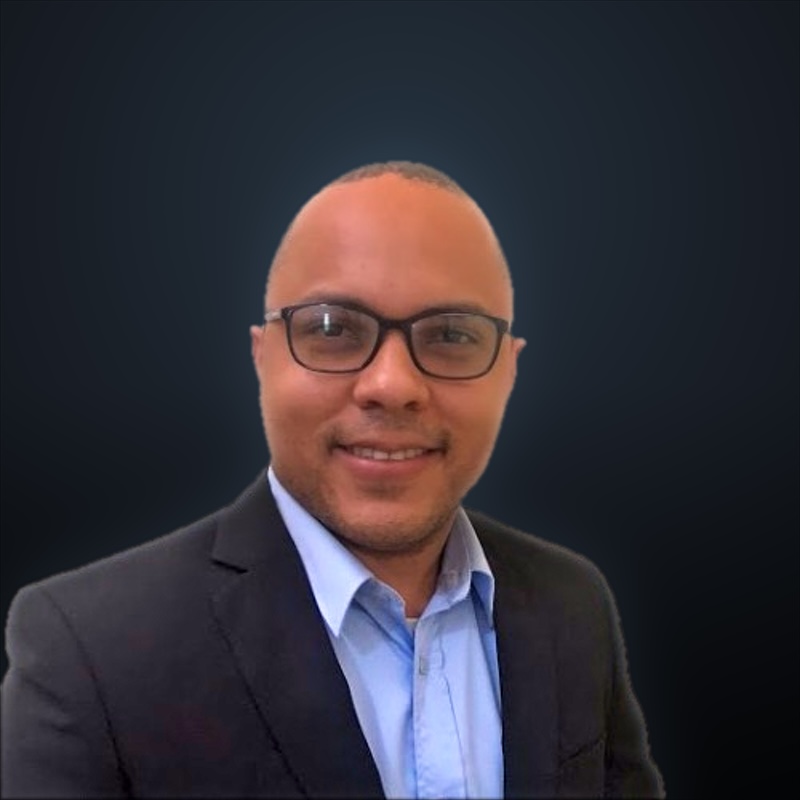
JM Sanchez
Technical Product Lead, Solutions Architect and Head of Systems & Data EngineeringI take platform risk off the CEO’s desk. I have worked with data and systems for more than twenty years, and for the last twelve I have directed business-intelligence and engineering teams whose work covers five countries. I build systems meant to keep running, pass an audit, and cost a fraction of the managed-cloud version.
The short version
- What I do
- I own the technical line end to end (edge, compute, data, client apps and compliance) and lead the team that builds it. I stay close enough to the code to review it properly, which is what lets me lead specialists rather than only manage them.
- Where
- Twelve years directing BI, analytics and systems engineering for operations in the United States, Kenya, South Africa, the Philippines and the Dominican Republic, reporting to VP and C-level. I have also delivered data work for United Nations Development Programme projects.
- Results
- A voice assistant that starts speaking in under 500 ms. Infrastructure that runs for about $1,900 a month where the managed equivalent lists at $38,000. No personal data stored in plaintext.
- How I work
- Errors are never swallowed, tests run against a real database, every dependency is pinned to an exact version, and AI-assisted tooling is part of the whole team’s workflow.
- Contracting
- Through a US (Delaware) B2B entity, so there is no employer-of-record overhead on your side.
Two results
Both come from systems running in production. Each one opens to show how it was done.
Time to first audible byte
Same model, same hardware, same data centre.
Monthly cost of the same workload
A voice assistant that starts speaking in under 500 ms. The usual pipeline takes 3 to 6 seconds on the same model and hardware.
A voice assistant chains four services: voice detection, speech-to-text, a language model and text-to-speech. Run them one after another and the user hears nothing for three to six seconds. Four changes brought the time to the first audible byte under 500 ms.
Change Effect One HTTP/2 connection for everything Audio chunks and control signals share a single bidirectional stream over Connect RPC. There is no WebSocket state machine and no round trip per frame. Voice detection on the device Silence is filtered on the client and never sent, so it is never transcribed or billed. Speech starts with the first sentence Synthesis begins on the first complete sentence and is forwarded through io.Pipewithout buffering. The user hears speech while the model is still writing.Interruptions stop the work When the user talks over the assistant, cancellation travels through context.Done()and stops generation and billing on the spot.Time to first audible byte Sequential pipeline, each stage waits for the previous one 3,000–6,000 ms Streaming pipeline described above < 500 ms Infrastructure that costs about $1,900 a month. The managed-cloud build of the same workload lists at $38,000, a difference of roughly $433,000 a year.
The same workload, costed two ways. The managed column uses typical published list prices for each tier and is meant as an order-of-magnitude comparison.
Managed-cloud build, per month Managed database cluster (Aurora Multi-AZ) $9,600 Managed Kubernetes and application compute $8,800 Managed cache and event streaming $5,400 Mirrored staging environment $5,200 Observability platform and security services $4,800 Load balancers, NAT and data transfer $4,200 Total $38,000 What runs in production, per month Stateless compute cluster, production and staging $1,100 Enterprise CDN, WAF, DNS and TLS $400 Persistent block storage, all nodes $260 Object storage and WAL archiving, multi-region $140 Managed database tier removed Load balancer and NAT tier removed Total $1,900 The production build is a stateless compute cluster with separate persistent volumes, a CDN edge and continuous WAL archiving. Production and staging are built the same way, so there is no configuration drift between them.
Dropping the managed database tier also drops a security boundary, so I replaced it with a stronger one: every personal-data field is encrypted with a KMS-issued key before it reaches the disk. A stolen database dump contains nothing readable. The reasoning is in decision D-03.
Four platforms
Systems I designed, built or led, and am still accountable for. Client and product names are withheld under confidentiality; I can walk through any of them in depth on a call.
Real-time voice AI platform. A conversational assistant that answers in under 500 ms.
The hard part
Four networked services (voice detection, speech-to-text, a language-model agent, text-to-speech) chained naively give three to six seconds of silence, a bill that grows with every syllable, and no way to interrupt the machine once it starts talking.
What I built
- Bidirectional HTTP/2 streaming over Connect RPC, with audio and control signals on one connection.
- Interruption through
context.Done(), which stops synthesis mid-sentence and stops billing with it. - Forwarding through
io.Pipewith no buffer, and synthesis one sentence at a time. - Two databases: personal and billing data in a managed vault reached over an mTLS tunnel, and analytics in a local PostgreSQL on a private network.
- Opaque session tokens in Valkey, with quota checks at the protocol boundary so a request over its limit fails before it costs anything.
Results
- Under 500 ms to the first audible byte.
- About 70% lower speech-synthesis cost, by changing the shape of the model’s responses.
- No human credentials exposed: the tunnel to the vault is outbound-only and machine-to-machine.
Go 1.26, Connect RPC, HTTP/2 (h2c), Protobuf, PostgreSQL with pgx v5, Valkey, Whisper speech-to-text, streaming text-to-speech, WebRTC voice detection, Caddy, Flutter.
Federated civic data platform. Works offline in the field, encrypts personal data before it touches a disk, and models three legal authorities that disagree with each other.
The hard part
Field operators across a whole country, often without signal, capture regulated personal data. That requires local writes that replay the same way every time, proof of who wrote what, authorization across national, regional and local levels that resolves in constant time, and a non-profit budget that rules out a managed multi-tier setup.
What I built
- An offline command queue: changes are written locally, signed with ED25519, and replayed on the server one record at a time, so one bad record never aborts a batch.
- AES-256-GCM envelope encryption with a KMS data key and a random 12-byte IV per field. The plaintext and the key are wiped from memory right after use.
- Access control by territory instead of flat roles, using prefix-encoded UUID trees so checking “is this record inside my region?” takes constant time.
- Three separate place registries (the international standard, national law and the cadastral authority), each frozen and versioned, linked by crosswalks instead of being forced into one hierarchy.
- Database triggers that make published reference editions impossible to edit, and seed tests that fail the build if provenance is broken.
- One Flutter codebase for iOS, Android, desktop and web, with SQLCipher and the hardware keystore on native devices and a non-extractable WebCrypto vault in the browser.
Go 1.26, Connect RPC, PostgreSQL 18, Valkey, AWS KMS, Flutter and Dart, SQLCipher, WebCrypto, OpenTofu, Hetzner Cloud, Caddy, WAL-G, Buf, Devbox.
Multi-national BI platform. One agreed set of numbers for operations, finance and executives in five countries, run by the 5-person team I manage.
The hard part
A large BPO operating in the United States, Kenya, South Africa, the Philippines and the Dominican Republic had its reporting spread across servers, spreadsheets and departments. Every executive review opened with an argument about whose numbers were right, and payroll, invoicing and incentive pay all depended on those numbers.
What my team and I built
- An Apache Superset rollout that became the single reporting source for executive leadership and operational governance.
- Automated ETL between servers in SSIS, Python and Power Query, feeding a central SQL Server, which cut report processing time by 40%.
- KPI and weighted-incentive frameworks for agents, supervisors, managers, directors and VPs, using the same definitions as the reporting.
- P&L reporting and forecasting models for C-level, and payroll and invoicing checked against revenue, billable hours and contract terms.
- Internal web systems built from design to adoption, including an MVC application for recording and auditing manual work hours, built to PCI-DSS and call-centre standards, and a company-wide quality-monitoring application.
Apache Superset, SQL Server, SSIS and SSRS, Python, Power BI, T-SQL, C# and .NET MVC.
Edge network with no permanent public IPv4 address. It attaches one for a few seconds to pull images, then releases it.
The hard part
An IPv6-only host cannot pull private container images from a registry that publishes no IPv6 (AAAA) records. The easy fix is a permanent public IPv4 address, which also means a permanent target for scanners. I kept the host IPv6-only and solved the pull problem instead.
What I built
- A temporary IPv4 address that attaches only for the image pull and detaches when a success hook fires. An earlier timer-based version removed routes mid-pull; the event-driven version cannot.
- A CDN origin certificate provisioned from code, which fixed an ACME challenge loop behind an always-HTTPS proxy with no manual console steps.
- Lifecycle separation: boot configuration changes no longer rebuild servers, database volumes and KMS keys are protected from deletion, and IP addresses no longer change when servers do.
- Short-lived registry credentials instead of personal access tokens, so there is no long-lived secret to store or leak.
- Deploys that poll for readiness, stop crash loops, probe outbound connectivity from inside the network and roll back automatically if verification fails.
Results: no permanent public IPv4 address, no long-lived registry secrets, and several minutes removed from every cold boot.
OpenTofu, Hetzner Cloud, Cloudflare (WAF, DNS, Origin CA), cloud-init, Docker Compose, GitHub Actions, Caddy, SOPS with age, Trivy.
Other work. United Nations Development Programme data projects, a live electoral data platform, and healthcare-compliance documentation.
- United Nations Development Programme. Data and analytics work on two projects, turning programme data into reporting the programme teams could use.
- Electoral data platform. Live vote-count pipelines connected to the national electoral authority’s data feed, plus a membership registration system and app. I led a team of one analyst and three developers as project and product manager, and handled the live data engineering myself.
- Healthcare compliance. Audited policy, procedure and licensing documents for a Texas-based healthcare-compliance company, under HIPAA, HITECH and the Stark Law. Every document is approved by a certified compliance specialist.
Decision log
These are the decisions I would defend in an architecture review: what I chose, what I turned down, and what it cost. I keep records like these in the repositories themselves, next to the code they affect.
D-01Speech synthesis one sentence at a time instead of
waiting for the full model response- Context
- A sequential voice pipeline leaves the user in silence for three to six seconds.
- Decision
- Stream over one multiplexed HTTP/2 connection and start synthesis on the first complete sentence.
- Consequences
- Under 500 ms to the first audible byte. Cancellation has to reach every stage, so every stage runs under a shared context.
D-02Opaque tokens stored in Valkey instead of
JWT sessions- Context
- A JWT cannot be revoked without a revocation list, and a revocation list is a session store under another name.
- Decision
- Use a real session store and keep tokens opaque.
- Consequences
- Instant revocation, smaller requests, and quota counting in constant time. One more stateful service to operate.
D-03Field-level encryption in the application instead of
a separate, segregated data tier- Context
- The budget could not pay for a segregated data tier.
- Decision
- Encrypt every personal-data field with AES-256-GCM using a KMS-issued data key before it reaches the disk, and wipe the key from memory after use.
- Consequences
- The database never holds readable personal data, even if it is copied. KMS is called only when a batch contains personal data, so key-service latency does not slow ordinary traffic.
D-04A self-hosted HA cluster, with staging built like production instead of
managed multi-tier cloud- Context
- The managed build of the workload lists at $38,000 a month.
- Decision
- Stateless compute nodes, separate persistent volumes, continuous WAL-G archiving and an enterprise CDN, with staging identical to production.
- Consequences
- About $1,900 a month, no configuration drift, and horizontal scaling by adding nodes. The team owns operations, so restore drills are automated instead of written down.
D-05A temporary IPv4 address during image pulls instead of
a permanent public IPv4 address- Context
- An IPv6-only host needed images from a registry without IPv6 records. A permanent address would be scanned permanently.
- Decision
- Attach an address for the pull only and release it from an event-driven success hook.
- Consequences
- No standing IPv4 exposure. The timing complexity this added was later removed by moving the teardown from a timer to the hook.
D-06Protobuf over HTTP/2 for every API instead of
JSON over REST- Context
- Server and client drift apart when each side writes its own request and response types.
- Decision
- Generate both sides from the same contract file, and do not allow JSON on the wire.
- Consequences
- A whole class of integration bugs disappears, versions change safely through field numbering, and payloads are smaller on slow mobile connections. Debugging needs tooling that can read the binary format.
D-07Hand-written SQL through a connection pool instead of
an ORM- Context
- Partitioned time-series reports have to stay predictable under load.
- Decision
- Write the SQL, generate typed code from it with sqlc, and run it through pgx.
- Consequences
- Query plans anyone can read and indexes anyone can reason about. More SQL to write and review.
D-08Tests against a real database instead of
mocked repositories- Context
- A mock confirms the code matches my assumptions. Only a real database confirms my assumptions match the database.
- Decision
- Integration tests run against real PostgreSQL, and CI fails if any test is skipped.
- Consequences
- Slower test runs, and no green pipelines that tested nothing.
D-09Every dependency pinned to an exact version instead of
floating tags such as:latestand@main- Context
- When there is an incident, the build that matters may be six months old.
- Decision
- Semantic versions or SHA-256 digests for containers, GitHub Actions, Go modules and infrastructure providers.
- Consequences
- Any past build reproduces byte for byte. Upgrades happen on purpose, through a reviewed change.
Why Go
Go compiles to one static binary, handles tens of thousands of concurrent connections on a single node, and treats every error as a value that has to be dealt with. The latency and cost results above depend on all three.
The field-encryption function from the civic data platform, with notes on what it shows.
internal/vault/seal.gopackage vault import ( "context" "crypto/aes" "crypto/cipher" crand "crypto/rand" "encoding/binary" "errors" "fmt" "io" "time" "go.opentelemetry.io/otel/attribute" "go.opentelemetry.io/otel/codes" "go.opentelemetry.io/otel/trace" ) // A version byte prefix lets keys or algorithms rotate later with no data migration. const ( envelopeV1 = 0x01 nonceSize = 12 // 96-bit GCM nonce ) // Sentinel errors — internal KMS/network detail never leaks to the caller. var ( ErrSeal = errors.New("vault: seal failed") ErrContext = errors.New("vault: context invalid or canceled") ErrEntropy = errors.New("vault: entropy source failure") ) // Seal encrypts one PII field with a per-record data key from KMS and returns a // self-describing envelope. The plaintext data key never outlives this call. func (v *Vault) Seal(ctx context.Context, plaintext []byte) (_ []byte, err error) { if len(plaintext) == 0 { return nil, fmt.Errorf("%w: empty payload", ErrSeal) } // One span per seal; success/error recorded on the way out. ctx, span := v.tracer.Start(ctx, "Vault.Seal", trace.WithAttributes( attribute.String("kms.key_id", v.keyID), attribute.Int("payload.bytes", len(plaintext)), )) defer func() { if err != nil { span.RecordError(err) span.SetStatus(codes.Error, err.Error()) v.metrics.SealErrors.Inc() } span.End() }() // Bound the call only if the caller gave us no deadline of its own. if _, ok := ctx.Deadline(); !ok && v.kmsTimeout > 0 { var cancel context.CancelFunc ctx, cancel = context.WithTimeout(ctx, v.kmsTimeout) defer cancel() } if err = ctx.Err(); err != nil { return nil, fmt.Errorf("%w: %w", ErrContext, err) } // KMS data key, with latency recorded for the SLO. start := time.Now() dek, err := v.kms.GenerateDataKey(ctx, v.keyID) v.metrics.KMSLatency.Observe(time.Since(start).Seconds()) if err != nil { return nil, fmt.Errorf("%w: generate data key", ErrSeal) } defer wipe(dek.Plaintext) // zeroed on every path, including panic block, err := aes.NewCipher(dek.Plaintext) if err != nil { return nil, fmt.Errorf("%w: new cipher", ErrSeal) } gcm, err := cipher.NewGCM(block) if err != nil { return nil, fmt.Errorf("%w: new gcm", ErrSeal) } // One allocation for the whole envelope. size := 1 + 2 + len(v.keyID) + 2 + len(dek.Ciphertext) + nonceSize + len(plaintext) + gcm.Overhead() out := make([]byte, 0, size) out = append(out, envelopeV1) out = binary.BigEndian.AppendUint16(out, uint16(len(v.keyID))) out = append(out, v.keyID...) out = binary.BigEndian.AppendUint16(out, uint16(len(dek.Ciphertext))) out = append(out, dek.Ciphertext...) // Reserve the nonce and fill it from the OS CSPRNG. ivStart := len(out) out = out[:ivStart+nonceSize] if _, err = io.ReadFull(crand.Reader, out[ivStart:]); err != nil { return nil, fmt.Errorf("%w: %w", ErrEntropy, err) } // Seal in place: ciphertext+tag land in the same backing array. out = gcm.Seal(out, out[ivStart:], plaintext, nil) return out, nil }- One binary. It ships in a distroless, non-root container with no runtime to install or patch, and starts in milliseconds. Each node in the cluster needs a small fraction of the memory a managed runtime would.
- Cheap concurrency. A goroutine starts with a few kilobytes of stack, where a thread-per-request runtime starts at about a megabyte. That is why live audio streams and background sync workers can share modest hardware.
- Errors that cannot be ignored by accident. With
errcheckas a merge gate, an unhandled error stops the pipeline, and production incidents arrive with a readable cause.
Security and compliance
I have worked under HIPAA, HITECH, the Stark Law, PCI-DSS and GDPR, and I build the cryptography as well as the policy documents. The compliance design is self-assessed against published standards and has not been certified by a third party. Where certification is required, I prepare the evidence an auditor needs and work alongside the assessor.
How personal data, identity, erasure and recovery are handled.
Envelope encryption
KMS issues a data key, the field is encrypted in memory with AES-256-GCM and a random 12-byte IV, and the database stores the encrypted key, the IV and the ciphertext together. The plaintext and the key are wiped immediately.
Identity
A device-bound handshake returns the session token, permissions, territorial scope and a server-derived local database key in one payload. Offline changes carry ED25519 signatures that are verified before replay. Vault database access uses certificates (mTLS), so there is no password to leak.
GDPR articles 9 and 17
Special-category data is never stored in plaintext. Erasure is built into the data model: records are keyed by UUID with deletion cascades, so erasing a person is one operation with a known reach.
Regulated delivery
A payroll and manual-hours application built and audited to PCI-DSS and call-centre standards. Ongoing documentation work under HIPAA, HITECH and the Stark Law for US medical practices.
Supply chain
Exact version pins everywhere, secrets encrypted at rest with SOPS and age, and Trivy, govulncheck, osv-scanner and go-licenses in the pipeline, including a check that no copyleft licence slips in.
Disaster recovery
Continuous WAL-G archiving to S3-compatible storage with automated restore drills. Deletion protection on persistent volumes and KMS keys, and explicit resource targeting so a rebuild can only touch the compute tier.
How changes ship
Every change goes from a feature branch through automated gates to a verified deploy. If any gate fails, the deploy rolls back on its own and the diagnostic probes stay in place.
The five gates, the incident loop and the rule for “done”.
Stage What happens Blocks the change if Branch Work happens on a feature branch, never on main.the pre-push hook fails Static checks golangci-lint,go vetandstaticcheckrun.any error is left unhandled Tests Integration tests run against a real PostgreSQL. a test fails or is skipped Image A distroless, non-root image is built, pinned by digest and scanned with Trivy and govulncheck. a tag floats or a scan fails Release A rolling deploy waits for readiness and probes outbound connectivity before taking traffic. verification does not pass After release
- Instrument first. Telemetry runs out of process through control-plane APIs, with no in-process agent.
- Detect early. Timeouts and health probes turn a slowdown into a signal instead of a silent hang.
- Diagnose in place, adding instrumentation rather than loosening security.
- Fix, then verify with live checks from beyond the CDN edge.
- Keep the probes that found the problem in the repository for next time.
When a change counts as done
Every error has context and a bounded timeout; real-database tests pass with none skipped; and a live check past the edge (TLS probe, authenticated RPC call, CORS preflight) succeeds. Then it merges from feature to develop to main, with rollback ready.
How I lead
From Santo Domingo I lead a business-intelligence and engineering team whose work reaches operations in five countries. Much of my week is spent between operations, finance, executive leadership and engineering, turning goals that each group defines differently into a roadmap all of them sign. I also designed the KPI and weighted-incentive frameworks used from agent to VP level, so performance is measured the same way the business pays for it.
I care about the people who ship the work as much as the architecture. A system the team cannot own will not last, however good it looks on paper.
My teams work under six rules, and the pipeline enforces them:
- No silent failures. Every error is wrapped with context. No empty catch blocks and no swallowed exceptions.
- A timeout on every network call, measured in seconds, with cancellation shared across the request.
- Verified before it is called done: TLS probes past the CDN, authenticated RPC calls, CORS preflight checks.
- Technical debt written down in the repository, where the next engineer will find it.
- Feature to develop to main, never straight to production, whoever is asking.
- Instrument before escalating. When something breaks we add instrumentation, not exceptions to the security model.
“A system that is up on modest hardware beats a correct architecture nobody can afford.”
Tools
The full toolkit, grouped by how much depends on each tool.
Production depends on these
- Runtime and protocol
- Go 1.26, Connect RPC, Protocol Buffers, HTTP/2 (h2c), gRPC, Buf, protovalidate, sqlc
- Data
- PostgreSQL 18, pgx v5, partitioned time series, PL/pgSQL, Valkey and Redis, SQL Server, Oracle, MySQL, SQLite and SQLCipher, WAL-G
- Security
- AWS KMS, AES-256-GCM envelope encryption, ED25519, mTLS, opaque tokens, SOPS with age, zero-trust network isolation
- Client
- Flutter and Dart for iOS, Android, desktop and web, offline-first sync, Isar, WebCrypto, Svelte 5, Astro 5, TypeScript
- Infrastructure
- OpenTofu and Terraform, AWS, Cloudflare, Hetzner Cloud, Azure, Google Cloud, Docker, Caddy, GitHub Actions, Linux
How the team delivers
- AI-assisted work
- Claude Code, Aider, OpenCode, Codex, Gemini AI Studio, automated test and lint loops
- Quality
- Devbox, golangci-lint, go vet, staticcheck, revive, govulncheck, osv-scanner, Trivy, go-licenses, ast-grep, Vitest
- Data and BI
- Apache Superset, SSIS and SSRS, Power BI and Power Platform, Python, Apache ECharts, MapLibre GL
- Network and operations
- Tailscale, WireGuard, Prometheus and Alertmanager, cloud-init, IPv6-only networks, Jira, Linear, ClickUp
Patterns that carry over to any stack
- Architecture
- Offline-first replication, a light CQRS command model, modular monoliths, stateless compute with separate persistent storage, disposable infrastructure defined in code
- Correctness
- Idempotent replay, at-least-once delivery with de-duplication, optimistic locking, immutability enforced by the database, bounded timeouts, cascading cancellation
- Practice
- Site reliability engineering, Scrum, test-driven development, architecture decision records, documented technical debt, spec-driven development, business analysis
Experience
| Years | Role | Organization |
|---|---|---|
| current | Product Manager, AI lead and principal developer on a 3-engineer team | Confidential product (under NDA) |
| 2022–now | Business Intelligence, Statistics and Reporting Manager | ERC Global CX, remote and multi-national |
| 2025–now | Healthcare Compliance Content Specialist, part time | Healthcare-compliance company, Texas (remote) |
| 6 months | General Manager, Product Manager and Scrum Master (contract) | Pharmaceutical enterprise projects, Dominican Republic |
| 2014–2022 | Statistics and Reporting Manager | ERC Global / Working Bees |
| 2012–2014 | Senior Analyst, then Reporting Team Manager | Laurus International, Santo Domingo |
| 2003–2010 | Lead Statistics Analyst and Department Lead | Amov International Teleservices (Claro / América Móvil), Santo Domingo |
What each role involved.
Confidential product, current
Principal developer on a three-person team, responsible for product direction and the AI architecture. The client is not mine to name.
ERC Global CX, 2022 to now
- Manage a 5-person BI and analytics team in Santo Domingo and the USA, and turned static reporting into a full business-intelligence practice.
- Own invoicing, payroll and performance-KPI data, consolidating production data from the USA, Kenya, South Africa, the Philippines and the Dominican Republic.
- Main technical contact for operations, finance and executive leadership; KPI frameworks, incentive models and P&L reporting go directly to VP and C-level.
- Moving the stack to open-source, AI-ready tools for faster data processing.
Healthcare compliance, 2025 to now
Research and write policy, procedure and licensing documents for US medical practices under HIPAA, HITECH and the Stark Law, each approved by a certified compliance specialist.
Pharmaceutical projects, six-month contract
Led a 6-person team of analysts and junior and senior developers across three products at once: geolocated BI, a Microsoft Power Apps solution and a SaaS platform with call-centre features. Owned the client relationship and designed the AWS layout (load balancing, EC2, network).
ERC Global / Working Bees, 2014 to 2022
Built the reporting function from performance dashboards up to executive P&L. Designed the databases, stored procedures and SSIS packages for automated ETL and transfers between servers, and owned the revenue, billable-hours and payroll calculations behind forecasting and budgets.
Laurus International, 2012 to 2014
Led three analysts as Senior Analyst, then managed the Reporting Team. Built SQL Server ETL for invoicing, payroll and operations KPIs, and cut manual processing time by 40% with automated reporting.
Amov International Teleservices, 2003 to 2010
Led a three-person statistics department covering operations statistics and reporting for international telecom accounts. Built databases, file servers, macros and real-time data-entry controls for distributed teams.
Education, languages and certifications.
- Education
- B.S. in Software Engineering, Universidad del Caribe (UNICARIBE), in progress. Professional technical degree in Computer Science, Politécnico Fabio A. Mota.
- Languages
- Spanish (native), English (full professional, C2), Italian (conversational).
- Engineering
- Site Reliability Engineering and Developing a Google SRE Culture (Google); Spec-Driven Development (Kiro / AWS); Clean Code with Go (CodeSignal); Mastering Design Patterns with Go.
- Business and leadership
- CBAP® exam preparation specialization (Coursera); Business Analysis: Key Definitions and Strategy Analysis (Starweaver); Effective Leadership Principles and Adaptive Leadership Principles (CodeSignal).
Questions
What does JM Sanchez do?
He is a Technical Product Lead, Solutions Architect and Head of Systems & Data Engineering. He owns the technical line end to end (edge, compute, data, client apps and compliance) and leads the team that builds it, with twelve years of business intelligence, platform architecture and site reliability work across five countries.
How is real-time voice AI delivered in under 500 ms?
A sequential pipeline (detect, transcribe, think, speak) makes users wait three to six seconds. Streaming over one multiplexed HTTP/2 connection and speaking each sentence as soon as it is ready, instead of waiting for the full language-model response, brings the time to the first audible byte under 500 ms on the same model, hardware and data centre.
How much cheaper is the self-hosted infrastructure than managed cloud?
About 20 times cheaper: roughly $1,900 a month self-hosted against $38,000 a month for the managed equivalent, with the same HA cluster, WAL-G backups, enterprise CDN and WAF, and full observability. That is about $433,000 saved per year.
How is personal data protected?
With envelope encryption in the application. Every personal-data field is encrypted with a KMS-issued key before it reaches the disk, so no personal data is stored in plaintext and someone who copies the database gets nothing readable.
Does JM work alone or lead teams?
He leads teams. He directs a business-intelligence and engineering team whose work spans five countries and has managed and grown people for twelve years. He stays close enough to every layer of the stack to lead specialists rather than only manage them.
What roles is JM looking for?
Head of Engineering, Technical Lead and founding-architect roles.
How can I get in touch?
Use the contact form on this page or send a message on LinkedIn. Every message gets a personal reply, usually within a day.
Contact
Tell me what you are working on: the latency target, the compliance requirement, the system nobody wants to touch, or the infrastructure bill. I read every message and reply personally, usually within a day. You can also message me on LinkedIn.
There is no email address or phone number on this site. The form sends your message to me directly over an encrypted connection.